+++ RECOMMENDED BY ZATAZ +++
"A book to devour without moderation. The central tension can be summed up in one sentence: collecting has become trivial, correlating has become vital."
- Damien Bancal, founder of ZATAZ.com, cyber-intelligence expert.
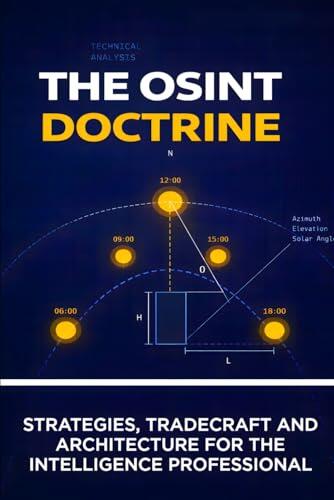
The OSINT Doctrine is not a tools guide.
It is a digital investigation engineering manual designed to turn traces into actionable and defensible intelligence.
After applying the method presented in this book, you will be able to:
• Map an individual’s lifestyle patterns by correlating public traces: sleep cycles, daily rhythms, activity windows, absence periods, probable movements, routines, behavioral shifts, and temporal anomalies.
• Reconstruct the digital identity of a person or organization from a single clue (username, image, email, technical detail), all the way to mapping their accounts, usage patterns, relationships, and exposure surfaces.
• Make infrastructure speak: pivot through entire networks from domains, IP addresses, certificates, and exposure history to identify dependencies, operational links, and real perimeters.
• Deconstruct a misleading narrative by demonstrating inconsistencies between images, videos, locations, and real-world facts - even without metadata.
• Geolocate a real-world scene from a photo using shadows, solar angles, terrain, vegetation, and urban features.
• Detect retouched and AI-generated images by analyzing pixels, altered areas, generation artifacts, and inconsistencies invisible to the naked eye.
• Conduct an investigation without exposing yourself by mastering your OPSEC, technical compartmentalization, and digital footprint control.
• Produce a clear, structured, and actionable intelligence report that transforms intuition into evidence-based proof.
CASE STUDY 01 - THE BLURRED FACE (Advanced IMINT)
Field: Counter-intelligence / Insider threat
Context: Sensitive code leak linked to a defense contractor
Clue: A single deliberately blurred photograph
CASE STUDY 02 - THE INVISIBLE STALKER (Identity Resolution)
Field: Executive protection / SOCMINT
Context: Anonymous blackmail targeting a senior executive
Clue: An empty Instagram account with no content or visible network
CASE STUDY 03 - THE GHOST INFRASTRUCTURE (Network OSINT / M&A)
Field: Due diligence / Supply chain
Context: Pre-acquisition audit of a company claiming to be “100% secure cloud-based”
Clue: A single public domain name
CASE STUDY 04 - THE DEEPFAKE WAR CRIME (GEOINT & Disinformation)
Field: Verification / Conflict / Information warfare
Context: Viral video accusing a state of a recent war crime
Clue: A short, emotionally charged video clip
CASE STUDY 05 - THE CRYPTO RUG PULL (FinINT / Blockchain)
Field: Financial intelligence
Context: Millions vanish following a fraudulent crypto project
Clue: A smart contract address
- Cycle: sourcing, analysis, transformation into evidence
- Technical layer: making infrastructure speak (DNS, logs, pivots)
- Real-world layer: GEOINT, forensics, deception detection
- Framework: OPSEC, ethics, investigator protection
Analysts, investigators, journalists.
LEVELWeb culture required. No hacking necessary.
INCLUDED250 pages, diagrams, Linux commands/code, report templates.
AUTHORRaphaël B., Linux SysAdmin and OSINT practitioner, ranked Top 50 FR on Hack The Box, approaches OSINT as a field-engineering discipline.
STOP LOOKING FOR MORE DATA. REVEAL WHAT IT SAYS.
ADOPT THE DOCTRINE.
Añadir una reseña
Su e-mail no será publicado. Los campos obligatorios estan señalados
Su puntuación *
Necesita Acceder a su cuenta o Registrarse